Sri Lankan organisations need to put data sovereignty frameworks in place and raise AI literacy across their workforces before the Personal Data Protection Act’s compliance regime takes effect in January 2027, a panel of industry figures has said, Hiru News reported.
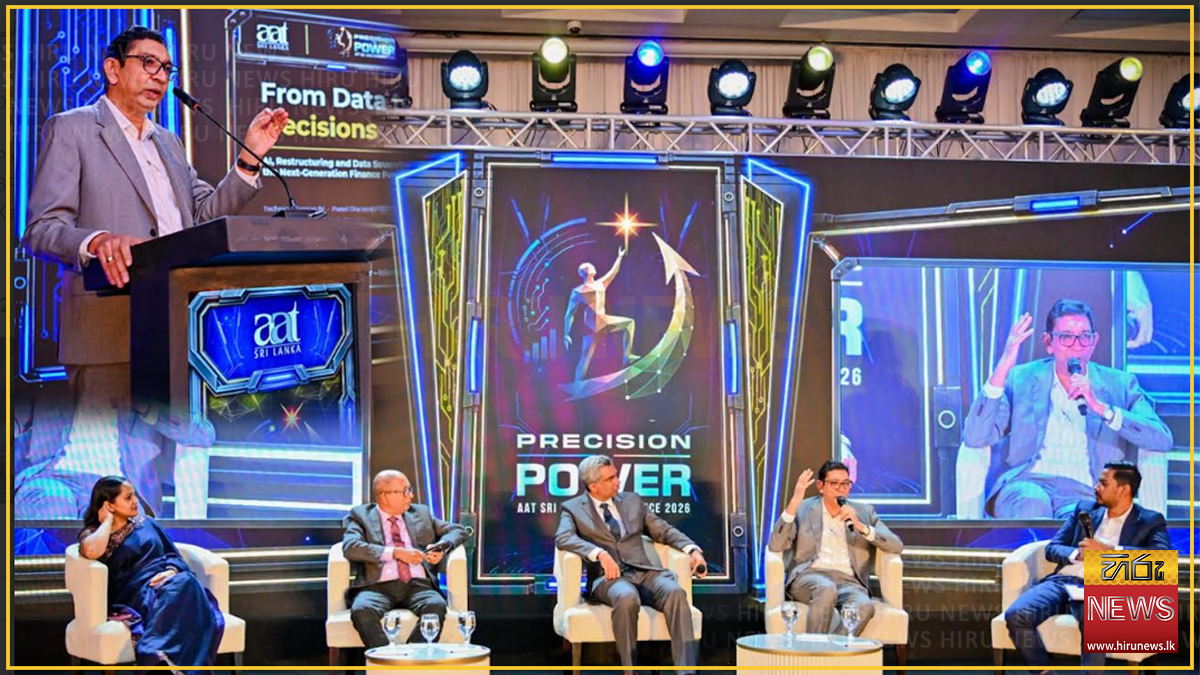
The remarks were made at a panel titled “Innovation, AI and Data in Finance: Data to Decisions”, held during the AAT Sri Lanka Conference 2026 at Waters Edge, Battaramulla, on 8 and 9 September. The session was moderated by Dehan Vithana, Lead Data Evangelist at MAS Holdings.
The infrastructure gap
The sharpest claim came from Sampath Jayasundara, CEO and Director of hSenid Business Solutions and chairperson of SLASSCOM, the IT industry body. Banks, hospitals and insurers, he said, need dedicated data sovereignty layers — while Sri Lanka’s domestic computing infrastructure remains insufficient for the AI processing load that is coming.
That is a straightforward statement of the problem a data sovereignty rule creates: a requirement to keep regulated data in-country is only workable if there is somewhere in-country to put it and process it.
Jayasundara’s prescription was architectural rather than aspirational — auditability, human-in-the-loop validation, and internal “Finance Brain” systems built on private large language model architectures rather than on external services. He also warned startups to watch AI running costs closely and to consider open-source tooling.
On employment he was blunt rather than reassuring: “AI will not replace people, but AI will replace people without AI.”
The figures cited
Jayasundara told the conference that 97% of finance departments had adopted AI in some capacity but only 42% had broadly or fully embedded it into core operations, and that finance teams spend roughly 90% of their time producing numbers — a share AI could cut to about 35%, freeing capacity for advisory work.
Citing the World Economic Forum’s 2025 report, he said 90 million traditional jobs could be lost globally while 170 million AI-transformed roles are created.
These figures are as reported by Hiru from the panel; LankaNewz has not independently verified the underlying studies, and the 97%/42% adoption split is not attributed to a named source in the filing.
Where the panel drew lines
Sanali Kaushalya, Country Director for Sri Lanka at Women in Tech Global, made the accountability argument in concrete terms: organisations should not let generative AI make sensitive decisions about employees or job candidates, and should not expose candidate material — CVs, photographs — to external AI models. Her alternative was internal tools governed by explicit ethical policies.
Anisha Dharmadasa, Managing Director of Nawaloka Holdings, said the group had adopted AI diagnostic technology early and seen gains in patient care and administration — while acknowledging the organisation was still working out what the incoming PDPA requires of it. That admission, from an early adopter in one of the most data-sensitive sectors, is the most telling line in the filing.
Professor Nuwan Kodagoda, Deputy Vice Chancellor of SLIIT’s Faculty of Computing, argued that AI literacy and the ability to critically evaluate AI-generated output are becoming baseline skills, and called on universities to move to annual curriculum updates rather than conventional four-year cycles.
One point of clarification
Hiru describes January 2027 as the “enactment” of the Personal Data Protection Act. The Act itself is already law; what is scheduled is the point at which the substantive obligations on data controllers and processors become enforceable. The distinction matters for organisations reading the date as the start of a drafting process rather than the end of one.
Note on sourcing, and on timing
This account rests on Hiru News alone. Daily FT separately covered the same conference — its filing on the keynote address, published 5 October, gives the conference theme as “Precision to Power” where Hiru renders it “Precision of Power” — but that report deals with different sessions and does not cover this panel, so it is not cited here as corroboration.
Readers should also note the gap between event and filing: the panel took place on 8 and 9 September, and Hiru published this account of it on 7 October.
Not reported
The filing does not say whether any Sri Lankan bank, hospital or insurer has actually built a data sovereignty layer, what domestic data-centre capacity exists or is planned, or what the PDPA requires on cross-border data transfer. No regulator is quoted, and there is no response from the Data Protection Authority or from government on the computing-capacity claim.
Source: Hiru News.